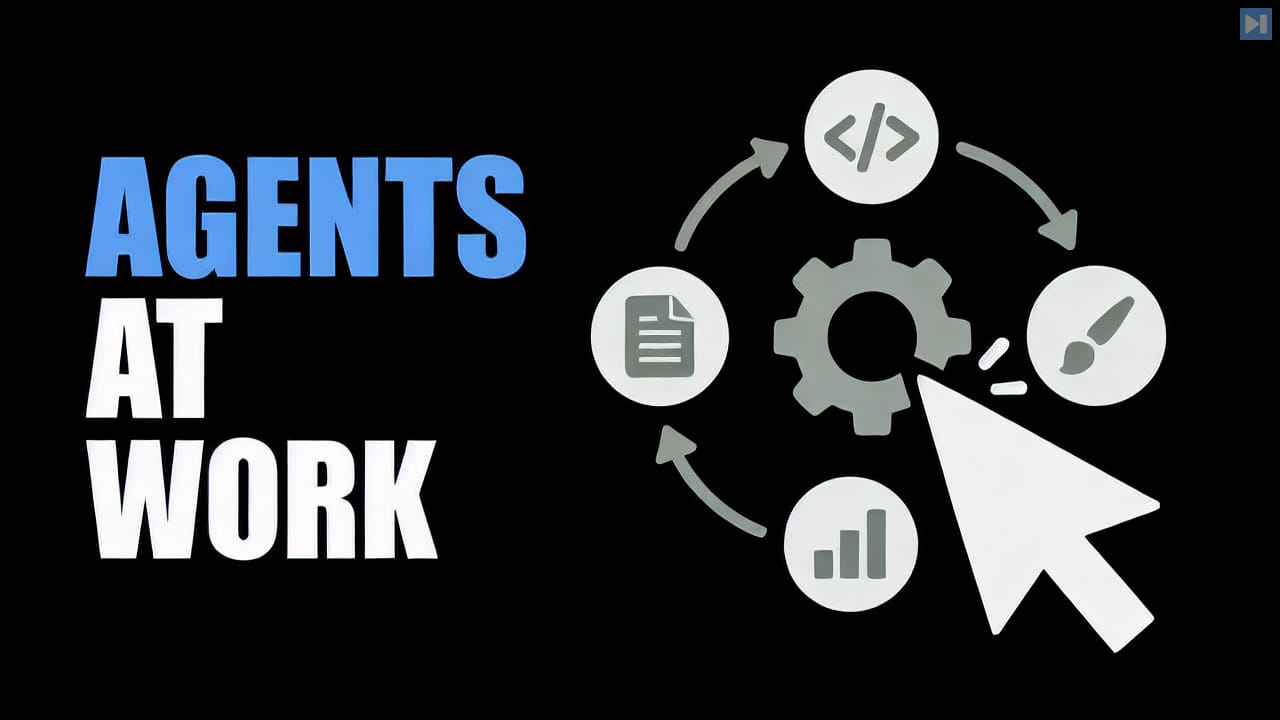
Agent tool use connects model decisions to defined operations such as reading a file, querying a service or running a command. A tool contract describes inputs, outputs and limits so the agent can choose and call the capability in a structured way.
Tools expand what an agent can accomplish, but they also create side effects and security risk. Systems should validate arguments, enforce authorization, separate read-only and mutating actions and return clear errors for the next decision step.
ELI5
Agent tool use is like an AI helper choosing the right item from a toolbox. It must know which tool fits the job and what to do with the result.
For example, the helper might use a browser to gather facts, a spreadsheet to organize them, and a drawing tool to make a chart, checking each result before moving on.
What is the difference between a model response and a tool call?
A model response generates content, while a tool call requests an external operation that can retrieve data or affect another system.
How should agent tools be secured?
Tools should validate inputs, enforce narrow permissions, protect secrets, report side effects and require stronger controls for consequential actions.